
Contents
- 1What Exactly Should Be Hidden from an Attacker
- 2How WordPress Behaves Out of the Box
- 3How to Make the Default Form Respond Consistently
- 4CAPTCHA Is Useful, but It Does Not Solve the Problem
- 5Why Rate Limiting Fits Here
- 6The Reset Form Is Not the Only Enumeration Channel
- 7Where Per-User Restrictions Make Sense
- 8What to Do About Operational Access
- 9A Minimal Check After Implementation
The “Lost your password?” form looks safe by default: a user enters a username or email, WordPress sends a message, and access is restored. That is how the official WordPress documentation describes the standard flow. For an attacker, though, the same form is a convenient tool for account enumeration: all it takes is comparing how the site reacts to a real user and a made-up one.
The difference is not limited to the text on the screen. It can hide in the HTTP status code, response size, redirect, processing time, or the behavior of the mail chain. If any one of these details differs, an account enumeration channel already exists. That is why a secure password reset is not a single patch but a set of coordinated decisions.
Key takeaways
- The default WordPress form shows “There is no account with that username or email address”, which directly confirms whether an account exists.
- OWASP recommends the same message and the same response time for existing and non-existing accounts.
- Check not only the text but also the HTTP status, redirect, response size, timing and mail errors.
- CAPTCHA and rate limiting make mass attacks harder, but they do not remove the leak itself.
- Per-role reset restrictions must not produce a different response from a normal request.
What Exactly Should Be Hidden from an Attacker
The OWASP Forgot Password Cheat Sheet sets two basic requirements: return a consistent message for both existing and non-existing accounts, and make sure the response time is uniform. This is not about “deceiving” the user but about minimizing signals. The wording should stay neutral, for example: “If an account with these details exists, we will send instructions to the associated address.” The user gets a clear next step, while the site does not confirm that a profile exists.
Response time matters just as much. If for one email the system looks up the user, generates a key, builds and sends a message, but for another it finishes almost instantly, that difference can be measured with a series of requests. So the “negative” scenario should not finish noticeably faster than the positive one.
Which Signals to Compare During an Audit
- the message text shown after the form is submitted;
- the HTTP status and redirects;
- the response body size;
- response time for an existing and a non-existing account;
- differences in application and mail server logs;
- errors that occur in only one of the two scenarios.
If you are testing a theme, plugin, or custom endpoint, do not stop at a visual check. User enumeration often lives not in the interface but in technical details a regular user never sees.
How WordPress Behaves Out of the Box
It is important to have no illusions here: the default WordPress password reset form is not protected against account enumeration. The retrieve_password() function that handles the request returns the error “Error: There is no account with that username or email address.” for an unknown username or email. For an existing account, WordPress sends the message and redirects to the checkemail=confirm screen. The difference is visible without any tools at all.
There are less obvious signals too. If password reset is disallowed for a specific user, core returns a separate message, “Password reset is not allowed for this user”, which confirms the account exists. And if the message fails to send (for example, SMTP is broken), the sending error appears only for real accounts. On top of that, a theme may output its own flash messages, and third-party forms have their own logic: in WooCommerce, for instance, the “Lost your password?” form in the customer account is handled by separate code, so it needs to be tested on its own.
Check your site in two minutes
- Open the “Lost your password?” form in a private browser window (use your custom login URL if you changed it).
- Enter an obviously made-up email and note the response.
- Repeat with a test account that definitely exists.
- If the text, page URL or behavior differ, the form reveals which accounts exist on the site.
- If you run a store, repeat the same test with the WooCommerce “My account” form.
How to Make the Default Form Respond Consistently
The simplest step for wp-login.php is to show the same screen whether or not an account was found. Below is a basic example using the lostpassword_post hook, which WordPress fires while processing the request. The code targets WordPress 6.3+; put it in a site-specific plugin or a child theme’s functions.php, and always test it on staging first.
<?php
/**
 * Neutral response for the core "Lost your password?" form (wp-login.php).
 * Requires WordPress 6.3+ (wp_is_password_reset_allowed_for_user).
 */
add_action( 'lostpassword_post', 'wsp_neutral_lostpassword_response', 10, 2 );

function wsp_neutral_lostpassword_response( $errors, $user_data ) {
    // Only the core form: WooCommerce and other plugins use their own handlers.
    if ( empty( $GLOBALS['pagenow'] ) || 'wp-login.php' !== $GLOBALS['pagenow'] ) {
        return;
    }

    // An empty field is an input error, not a signal about an account.
    if ( in_array( 'empty_username', $errors->get_error_codes(), true ) ) {
        return;
    }

    $hide_result = ! $user_data || true !== wp_is_password_reset_allowed_for_user( $user_data );

    if ( $hide_result ) {
        // The same screen core shows after a successful request.
        wp_safe_redirect( add_query_arg( 'checkemail', 'confirm', wp_login_url() ) );
        exit;
    }
}
With this in place, for a non-existing account, as well as for one where reset is disallowed, the user sees the same “Check your email” screen as after a successful request. To be honest about the limits: this code aligns the text and the redirect, but not the timing. For a real account WordPress still generates a key and sends the message, so the response may take slightly longer. To remove that signal too, send the email asynchronously (via a queue or a background job) and return the response equally fast in both cases.
Rule of thumb: the form should respond the same way to any input, and everything that depends on whether an account exists — the lookup, the key, the email — should happen in a way that is invisible from the outside.
CAPTCHA Is Useful, but It Does Not Solve the Problem
The OWASP Authentication Cheat Sheet treats CAPTCHA as a defense-in-depth control: it makes automated attacks slower and more expensive, but it is not a standalone protection. The same applies to the reset form: CAPTCHA can make mass scanning harder, but if the form responds differently, every successful request still confirms that an account exists.
So the order should be: first make responses identical, then add frequency limits, and only after that, if needed, strengthen protection with CAPTCHA or other checks. Starting with CAPTCHA while leaving different text or different timing in place only postpones the problem.
Why Rate Limiting Fits Here
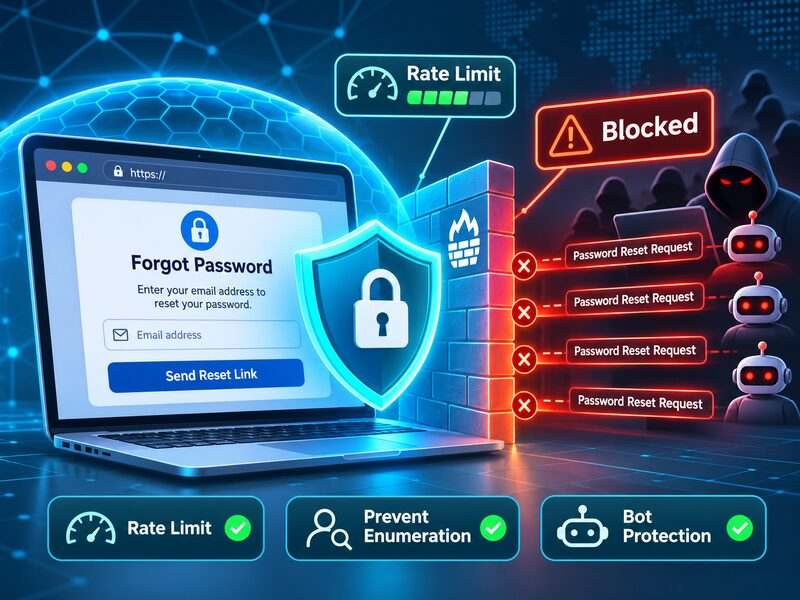
Limiting attempt frequency does not remove enumeration on its own, but it reduces the scale of an attack and gives you time to notice scanning. NIST SP 800-63B requires limiting failed authentication attempts (rate limiting), and the same logic naturally carries over to the reset form: unlimited requests mean unlimited scanning. For WordPress, this means the password reset URL should not be left uncontrolled at the web server, Cloudflare/WAF, or security plugin level.
In practice, it helps to limit not only the total number of requests but also anomalous repetition from a single source. At the same time, do not turn protection into a new leakage channel: if the form starts reacting differently to a “suspicious” and a “normal” email, it helps the attacker again. The limit should trigger the same way regardless of whether the account exists.
The Reset Form Is Not the Only Enumeration Channel
Even a perfectly configured form will not help if usernames are visible elsewhere. On a default WordPress install, check:
- The login page — by default it reports an unknown username and a wrong password differently.
- Author archives — a request to
/?author=1redirects to/author/username/when the author slug matches the login. - The REST API —
/wp-json/wp/v2/userslists authors with published posts, including their slugs. - The sitemap — since WordPress 5.5, core generates a users sitemap (
wp-sitemap-users-1.xml).
What to close depends on the site: for a blog with public authors, archives are normal, while for an online store or a customer portal it is better not to expose logins. We covered the broader topic of how access-check mistakes expose other people’s data in our article on Broken Access Control in WordPress.
Where Per-User Restrictions Make Sense
WordPress 6.3 introduced wp_is_password_reset_allowed_for_user(). It checks whether a specific user may reset their password, and the result can be changed via the allow_password_reset filter — for example, to disable form-based resets for administrators. This is a useful tool for access policies, but caution is needed: as shown above, core answers a disallowed request with a separate message, and that message tells an observer the account exists.
So any special policy must be tested for identical external behavior: messages, response codes, redirects and delays. A user should not see a different response just because a different policy applies to a certain role or group. The code example above handles this case exactly like a non-existing account.
What to Do About Operational Access
When access has to be restored manually, for example during an incident, use tools that go through WordPress’s own internals rather than editing the database by hand. The official documentation lists WP-CLI among the ways to reset a password, and the wp user reset-password command generates a new password for one or more users (with the --skip-email and --show-password options). For a support team this is especially handy: there is no need to invent “workaround” procedures that are hard to control later.
Also keep in mind the general practices that reduce the impact of a compromise: strong passwords, HTTPS, timely updates and two-factor authentication. They do not remove account enumeration through the reset form, but they make a discovered username far less valuable to an attacker.
A Minimal Check After Implementation
After making changes, run a short security test: several requests for an existing and a non-existing username and email, plus one for an account where reset is disallowed. Compare the response body, headers, redirects, response time and email behavior. If even one parameter differs without a good reason, fix it. What matters here is not perfect theory but practical control of the real form in the real environment.
It is also worth checking whether the infrastructure gives itself away: different redirects, mail errors, or how POST requests are handled at the CDN or WAF level. The small differences that make enumeration possible most often appear exactly where the theme, plugins and mail server meet.
Secure password reset checklist
- The same neutral message for any username or email entered.
- The same HTTP status and the same redirect in both scenarios.
- The email is sent asynchronously; response time does not depend on whether the account exists.
- Per-role reset restrictions do not produce a separate message.
- Mail errors are logged but not shown to the visitor.
- The reset URL is rate limited, identically for all requests.
- The WooCommerce form and any other custom login forms are tested separately.
- The login page,
?author=, the REST API and the sitemap do not expose usernames unnecessarily.
A secure password reset in WordPress is not one magic function but a discipline of consistent behavior. When the form responds neutrally, the timing does not “jump”, and operational procedures do not create extra signals, it becomes much harder for an attacker to tell which accounts are real. If you would rather not check all of this yourself, it is part of regular technical maintenance — for example, WSP Care — WordPress maintenance services.